Centralized Identity & Single Sign-On Gateway
Universal OAuth 2.0 & OpenID Connect authentication broker. Unifies federated social logins, client domain validation, and single-use cryptographic token exchange across connected applications.
Core Gateway Services
Operational infrastructure for cross-origin identity delegation, application registration, and token exchange.
Federated Identity Brokerage
Proxies authentication requests between downstream client applications and upstream identity providers (Google, Apple, Meta, GitHub, Microsoft). Client sites authenticate via one central broker without configuring separate vendor consoles.
Domain & Tenant Management
Organizes client applications into isolated tenant workspaces. Allows team collaborators to manage authorized redirect URIs, CORS origins, and API client keys with granular access control.
Single-Use Atomic Ticket Exchange
Issues short-lived 60-second authorization tickets cryptographically signed by the broker. Spoke backends exchange tickets server-to-server for verified user claims via atomic burn-on-read validation.
Admin Impersonation & Diagnostics
Enables authorized administrators to inspect registered domain entity graphs, audit active collaborators, monitor webhook delivery status, and safely impersonate accounts to reproduce support inquiries.
Identity Profile Persistence
Maintains persistent records of provider-assigned unique subject IDs, primary verified email addresses, and full name attributes for customer identity synchronization across portfolio applications.
Signed Webhook Relays
Dispatches tamper-proof, HMAC-SHA256 signed event payloads to registered consumer endpoints whenever users authenticate, link providers, or update profile information.
Upstream Identity Provider Health
Live telemetry and operational status for connected third-party authentication services.
Federated Hub-and-Spoke Architecture & Authentication Flow
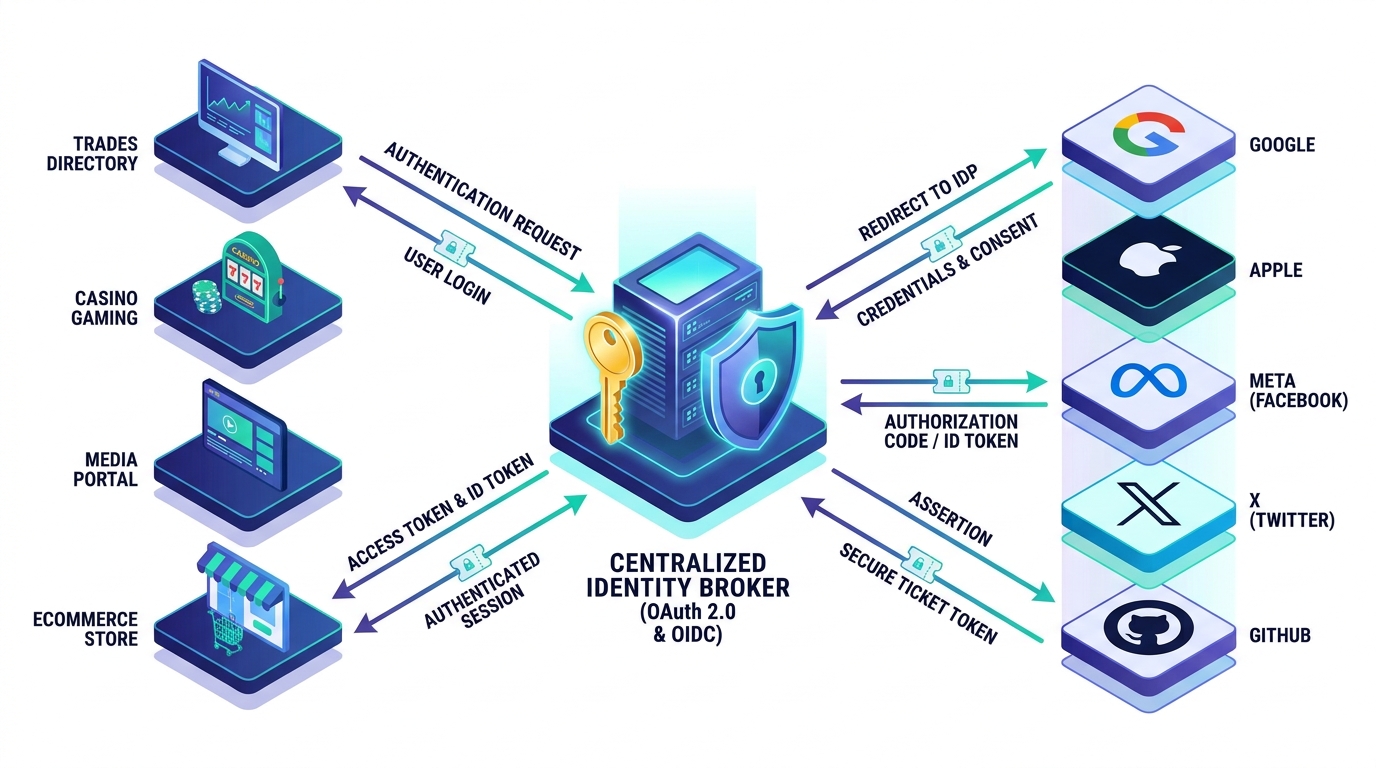
NoctisID decouples client websites from upstream social providers through high-speed edge token brokering.
Zero Upstream Vendor Overhead
Child sites never register developer accounts with Google, Apple, or Meta. Exactly one master app per provider is configured at the broker root.
60-Second Atomic Ticket Burn
Client backends exchange short-lived cryptographic tickets for verified user claims via atomic burn-on-read validation, eliminating replay attacks.
100% Unique Domain Isolation
Every connected child domain is globally indexed with strict callback origin whitelists, preventing hijacking across tenant boundaries.
Standards & Specifications Compliance
NoctisID adheres to open standards defined by the IETF and the OpenID Foundation.
OAuth 2.0 Authorization
Standardized authorization code delegation flow with secure redirect parameters and state nonce verification.
OIDC Identity Layer
Identity claim assertions, UserInfo endpoint responses, and standardized ID token payloads.
PKCE Flow
Proof Key for Code Exchange preventing authorization code interception on public and single-page apps.
JSON Web Tokens (JWT)
Cryptographically signed identity assertions with JWKS public key verification.
Developer Integration Guide & Multi-Language SDKs
Ready to integrate a child website, WordPress theme, or microservice? Raw API gateway endpoints, OIDC parameter specs, and ready-to-run SDK code samples (WordPress / PHP, Node.js / Express, Python / FastAPI, and Frontend JS) have been consolidated into our dedicated developer documentation hub.
Cross-Origin Handshake Protocol Diagnostic
Diagnostic overview of the token delegation and verification cycle between client sites and the broker.
Client initiates authorization request with public client_id, provider, and state nonce.
Broker validates origin whitelist, proxies upstream provider authentication, and returns single-use 60s ticket.